


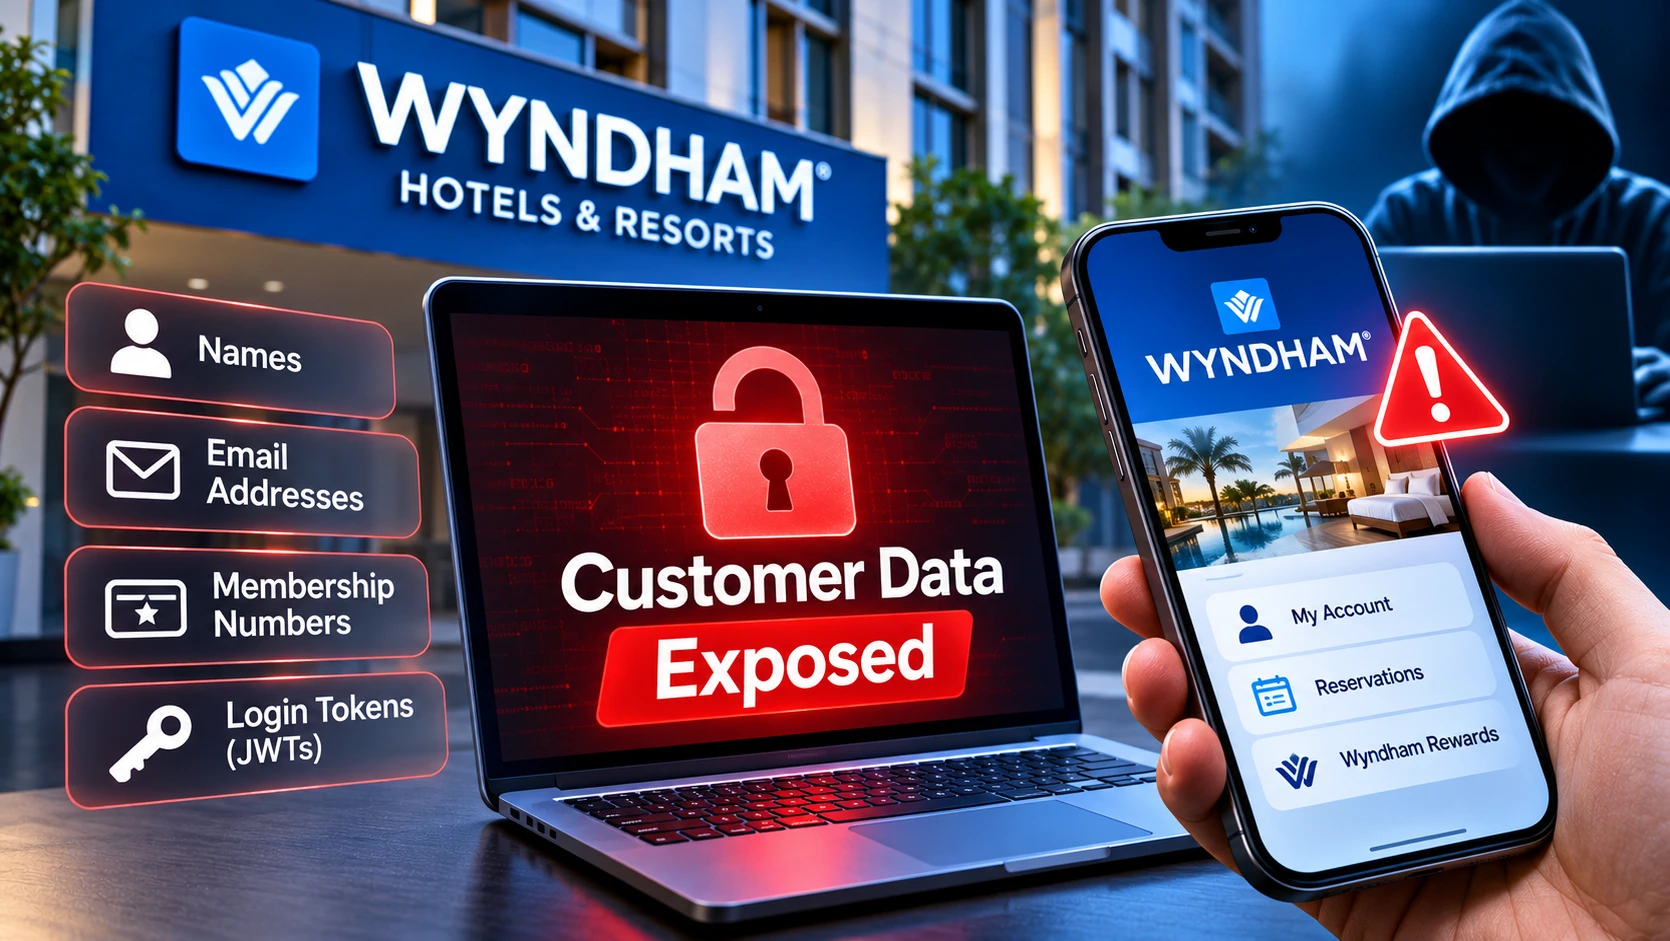
Wyndham Hotels & Resorts has addressed a security vulnerability that potentially exposed millions of customer records after a cybersecurity researcher discovered sensitive company credentials hidden inside its Android application.
The issue was identified by independent security researcher Robert Wiggins of What Security. He found a password embedded in the app’s source code that provided access to an internal database hosted on Salesforce infrastructure.
The exposed database contained customer information, including names, email addresses, and Wyndham Rewards membership numbers. It also stored login authentication tokens and internal company files.
A Password Hidden Inside the Android App
According to Wiggins, the security weakness was relatively straightforward to identify. A credential had been included directly in the publicly distributed Android application, allowing anyone who extracted the app’s code to retrieve it.
Using that password, the researcher was able to access an internal database containing millions of entries.
One particularly concerning detail was the presence of JSON Web Tokens (JWTs). These authentication tokens allow users to remain signed in to their accounts without repeatedly entering their passwords.
If exposed or misused, such tokens can create additional security risks beyond the disclosure of basic customer information.
Wiggins could not establish exactly how many customer records were accessible. However, Wyndham says its rewards program has approximately 129 million enrolled members, highlighting the potential scale of the exposure.
Wyndham Disabled the Exposed Credentials
Wiggins initially struggled to report the vulnerability because he could not find a clear security reporting process on Wyndham’s website.
He subsequently requested assistance in contacting the company’s security team.
After Wyndham was alerted, its cybersecurity staff revoked the exposed credential, blocking further access through the compromised password.
A company spokesperson confirmed that steps had been taken to address the problem and said there was no evidence of unauthorized access.
However, Wyndham did not clarify whether its technical teams had reviewed server logs to determine if anyone had accessed the database before the researcher discovered the vulnerability.
The company also declined to explain whether affected customers would be notified or whether the incident would be reported to relevant U.S. regulators.
Other unanswered questions include how long the password had remained inside the Android application and what permanent changes Wyndham plans to introduce to prevent similar problems.
Why Hardcoded Passwords Are a Serious Security Risk
Including passwords, API keys, or other sensitive credentials directly inside publicly distributed software is a well-known development mistake.
This practice, commonly called hardcoding, can give attackers a direct route into systems that were never intended to be publicly accessible.
Once an application is released, its code can often be examined and reverse-engineered. Even if developers attempt to hide credentials, determined researchers or attackers may still be able to extract them.
That is why security professionals recommend keeping sensitive credentials on protected server-side systems rather than embedding them in mobile applications.
Wyndham’s incident demonstrates how a seemingly small development oversight can potentially expose large amounts of customer information.
The Researcher Found a Similar Problem at Applebee’s
This was not Wiggins’ first discovery of this type of vulnerability.
Just two weeks earlier, he identified a similar security issue in Applebee’s mobile application, where an embedded database password exposed customer information.
Interestingly, he used AI-powered tools during both investigations.
These tools helped him examine large amounts of decompiled application code and identify potentially dangerous credentials much faster than traditional manual inspection.
As AI-assisted security research becomes more accessible, developers may face increased scrutiny of vulnerabilities that could previously remain unnoticed for years.
Wiggins welcomed Wyndham’s decision to disable the exposed credential but raised concerns about the lack of information regarding previous database access.
Without a clear picture of historical activity, it remains difficult to determine whether malicious individuals accessed or copied customer information before the vulnerability was fixed.
Wyndham’s Security History Raises Further Questions
The latest incident adds to Wyndham’s previous cybersecurity concerns.
In 2024, researchers discovered remote-access spyware installed on several hotel check-in computers. The software was reportedly transmitting screenshots containing guest records and booking information to publicly accessible locations.
The spyware, known as pcTattletale, was later hacked, resulting in the theft of data stored by the service. Its owner, Bryan Fleming, was subsequently arrested and convicted of making, selling, and advertising unlawful spyware.
These earlier events make the latest discovery particularly concerning, especially for customers who trust hotel companies with their personal and travel information.
What Happens Next?
Although Wyndham says it has addressed the immediate vulnerability, several important questions remain unanswered.
The company has not confirmed how long the exposed password was available, whether customer records were accessed before the fix, or whether affected users will receive formal notifications.
The incident also highlights an important lesson for software developers: mobile applications must never contain credentials that provide unrestricted access to internal company databases.
For businesses handling millions of customer records, fixing a vulnerability is only part of the responsibility. Understanding whether information was previously accessed and being transparent with affected customers are equally important parts of responding to a security incident.


